I break things to understand how they hold together.
I’m Selim Celebi, an offensive security engineer in Brussels. I test web applications, networks and systems, analyse malware and reverse binaries. I graduated cum laude from Howest in Applied Computer Science, on the Cyber Security Professional track.
Open to offensive security roles, in Brussels or remote.
Track record
| Event | Result | Year |
|---|---|---|
| Aviation CTF, EUROCONTROL | Co-engineered the competition. 113 players from 34 organisations, in 28 teams | 2025 |
| TryHackMe Hackfinity Battle | #295 of 4,356 teams, top 7% | 2025 |
| HackTheBox Cyber Apocalypse | #614 of 8,129 teams, top 8% | 2025 |
| Cyber Security Challenge Belgium | Four editions in a row | 2023 to 2026 |
| Hack the Future, Antwerp | Mission Among the Stars | 2024 |
The aviation CTF
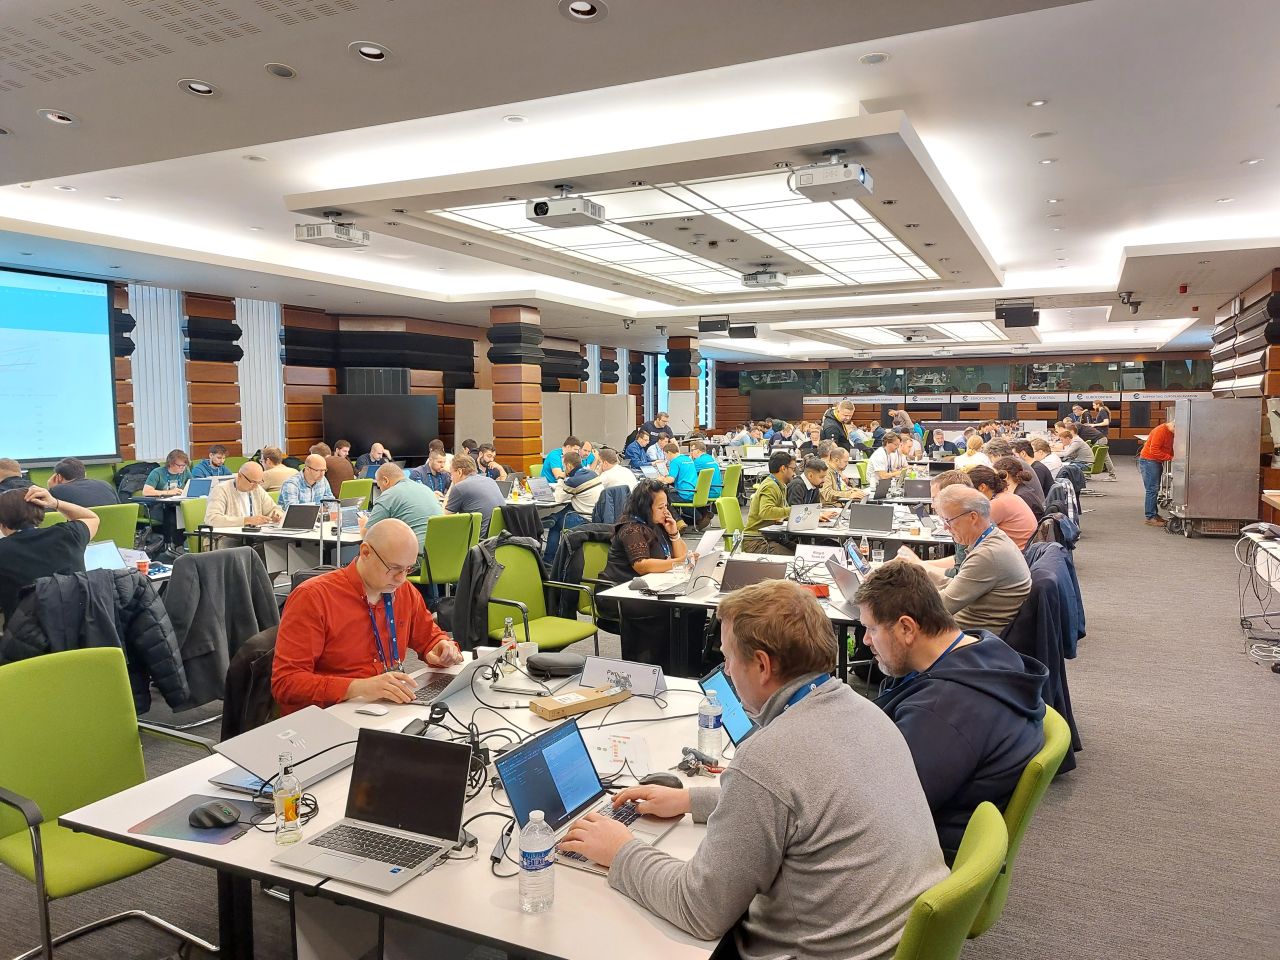
During my internship at EUROCONTROL’s EATM-CERT, the security team for European air traffic management, I co-engineered the 2025 Aviation Capture the Flag. It was played by 113 cybersecurity experts from 34 organisations, split into 28 teams: airlines, airports, air navigation service providers and civil aviation authorities. EUROCONTROL called it the biggest edition so far.
What I do
Penetration testing
Web, network and system assessments. My full audits of a company and a pharmacy covered OSINT, exploitation, a phishing simulation and a staff awareness survey, and ended in a report the client could act on.
Malware and reverse engineering
Static and dynamic malware analysis, binary reversing and digital forensics. I also built a deliberately vulnerable Android app as a training target for mobile pentesting.
Detection and deception
Honeypot servers wired to Kibana dashboards, run as a red versus blue exercise to see what the detection layer really catches.
Latest research
What I found auditing my own website
I pointed my own toolchain at this domain and treated it like a client engagement. Three findings made it to remediation:
- Fixed User enumeration through
/wp-json/wp/v2/users - Fixed Email address readable by scrapers in the page source
- Fixed Unencrypted HTTP still answering on port 80
Write-ups and field notes
-
What I found auditing my own website
I pointed my own toolchain at this domain and treated it like a client engagement. Three findings survived to remediation: a REST…
-
TryHackMe: Hackfinity Battle
TryHackMe’s student CTF: 65 tasks in 1,000 minutes. Our three-person team solved 45 and finished 295th of 4,356 teams, top 7%.
-
Cyber Apocalypse CTF 2025: Tales from Eldoria
Hack The Box’s annual CTF: 62 challenges in 11 categories. Playing with fellow EATM-CERT trainees and friends, we finished 614th of 8,129…
-
EU MITRE ATT&CK® Community Workshop 2025
Notes from the EU MITRE ATT&CK Community Workshop at EUROCONTROL: threat intelligence in action across the aviation sector.
-
Artifhacking Intelligence: When Hackers Meet AI
A live hacking show at Howest Bruges on where offensive security meets machine learning, and where the hype breaks down.
Hiring, or need a second pair of eyes?
I am looking for offensive security roles and engagements, in Brussels or remote. Messages go through a spam-protected form, so no email address is published here.