Work from my internship at EUROCONTROL and from my studies at Howest: competition design, security audits, a detection lab and mobile security. Write-ups for several of these are on the way.
Aviation CTF at EUROCONTROL
EATM-CERT is the computer emergency response team for European air traffic management. During my internship there I co-engineered the 2025 Aviation Capture the Flag, a competition built around aviation systems for security teams from across the sector. Designing challenges is the reverse of solving them: each one has to be unambiguous, solvable along the intended path, and closed to shortcuts nobody planned for.
113
cybersecurity experts played
34
organisations took part
28
teams competed
4
sectors: airlines, airports, air navigation, regulators
The event ran in December 2025 at EUROCONTROL’s headquarters in Brussels. Teams investigated incidents, analysed vulnerabilities and followed clues through an aviation scenario, and one challenge was physical: fly a drone through an obstacle, grab a key and bring it back to unlock the next step.
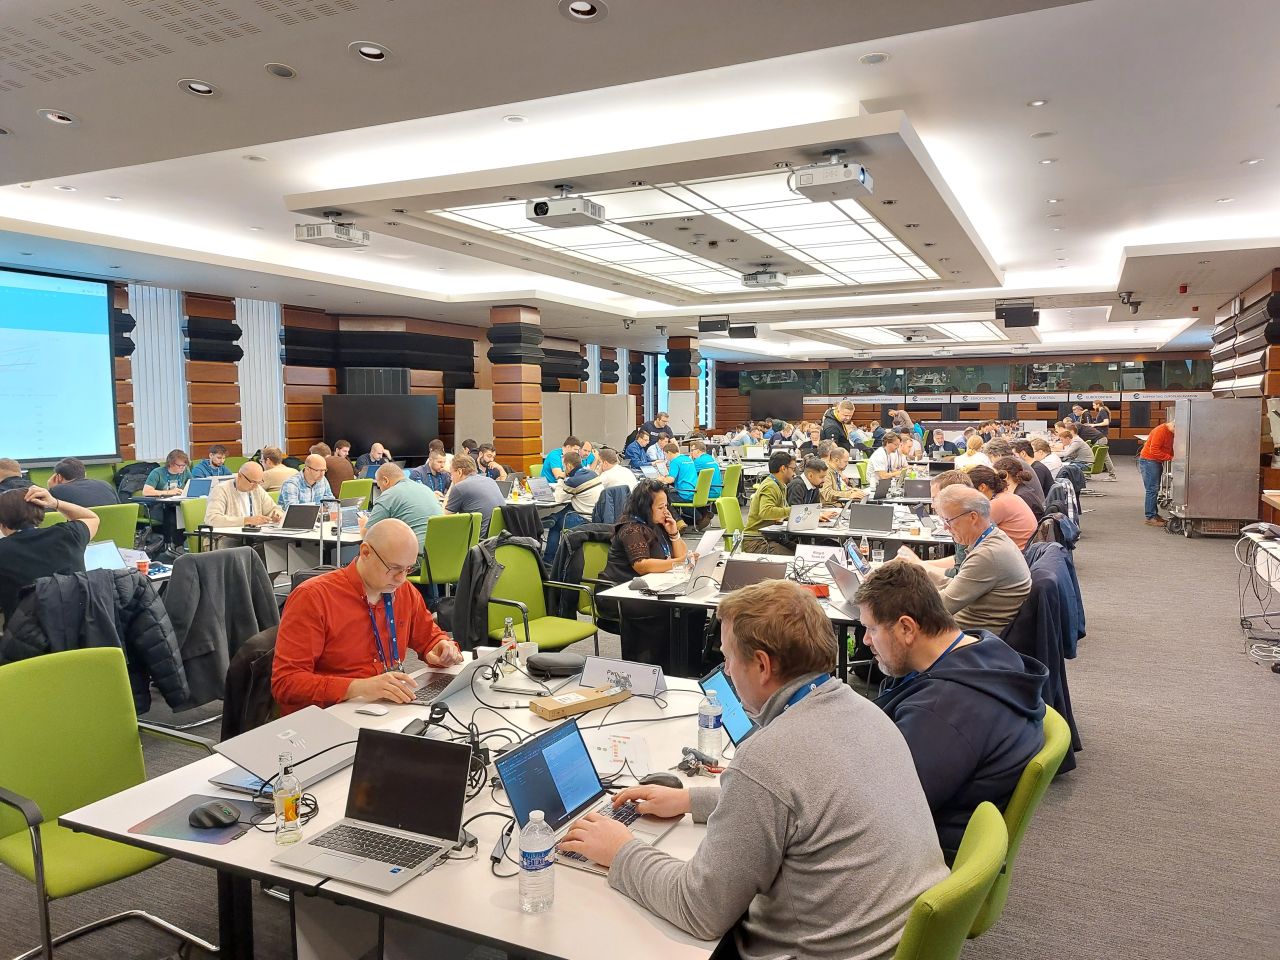
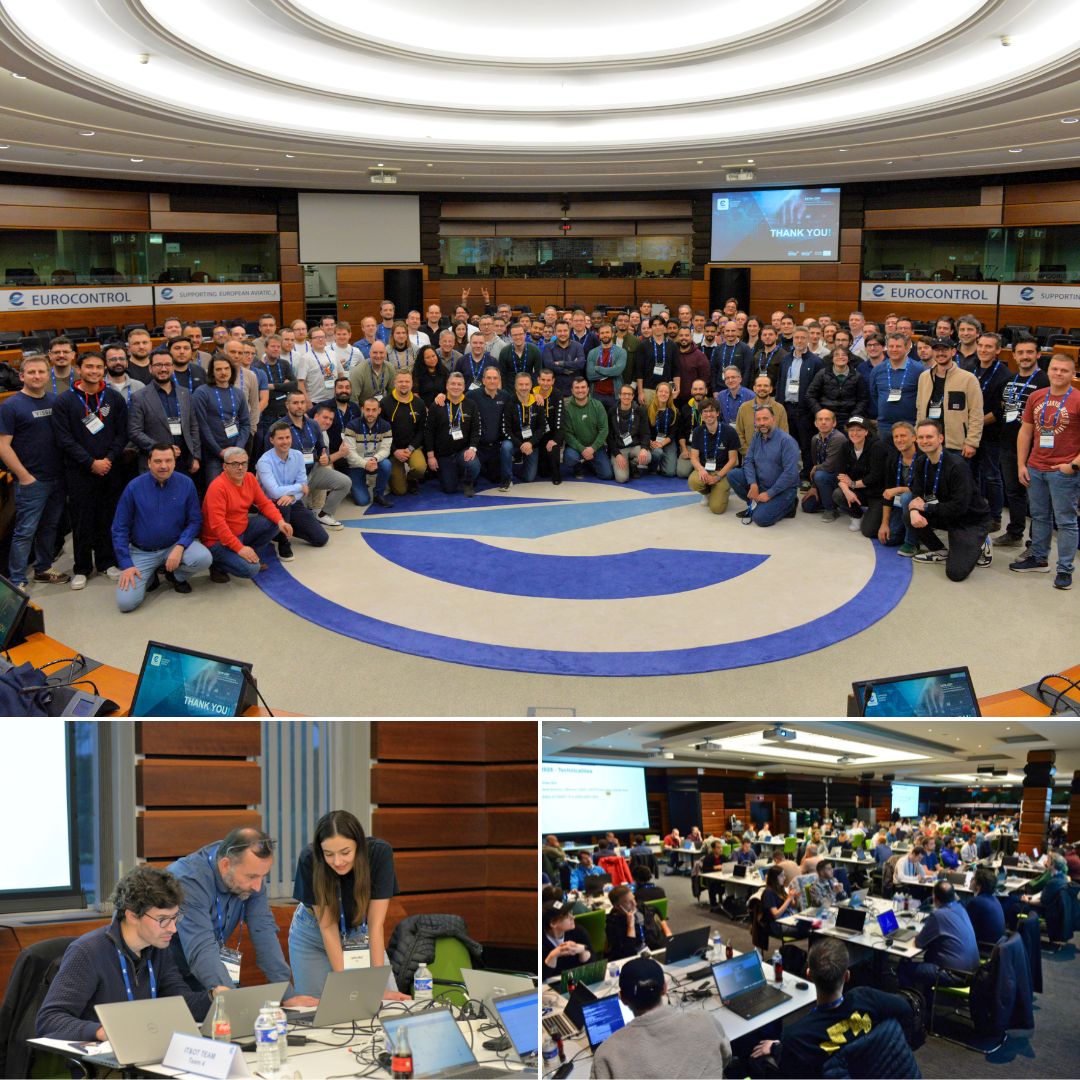
Alongside the CTF I carried out penetration tests on aviation systems and applications, and contributed to research on aviation cybersecurity.
Coverage
- EUROCONTROL on the 2025 edition: 113 experts from 34 organisations, the biggest edition so far.
- Patrick Mana, EATM-CERT manager, on the day: all 28 teams at work, and the drone challenge.
- EUROCONTROL on the 2024 edition, for scale: 24 teams and around 40 challenges the year before.
Full security audit of a company and a pharmacy
An end-to-end assessment of two real organisations: OSINT reconnaissance, technical penetration testing, a controlled phishing simulation and a staff awareness survey. The results went into a report with prioritised findings and a mitigation plan. As in most audits, people were the easiest way in.
Honeypot lab, red versus blue
I deployed honeypot servers and wired them to Kibana dashboards, then ran the setup from both sides: attacking the infrastructure, then reading what the detection layer had recorded. Comparing the two showed which attacks went unnoticed.
A deliberately vulnerable Android app
I built an Android application seeded with realistic flaws, such as insecure storage, weak authentication and poor certificate handling, as a training target for mobile penetration testing. Planting each flaw meant knowing exactly why it works and how it gets found.
Network and system pentest report
A full audit of a network and its hosts, written up as a professional pentest report with risk ratings and a mitigation strategy for each finding. I wrote it for the person who has to fix the issues, not for the person who found them.
Write-ups are published as I go. Read them on the blog, or see the full profile.